Stay Ahead of Cyber Threats with Expert Insights
Practical cybersecurity guidance, incident response expertise, and industry intelligence for Australian law firms and businesses.

The Legal Cyber Brief — monthly cyber intelligence for law firm leaders. Threats, regulatory shifts, and practical tools from the field. No fluff.
CYOODA - Newsletter
1,205 Breaches. A Record Year. And Your Sector Is a Fixture in the Top Five.
The privacy regulator just published the worst annual breach numbers since mandatory reporting began - and legal services made the most-affected list again. This fortnight: a record year the OAIC...

‘Months, Not Years’: The Five Eyes AI Warning No Law Firm Should Scroll Past.
Your next phishing email won't have a single typo - because a machine wrote it. This fortnight: an unprecedented Five Eyes warning that AI-powered attacks are close, a professional-services firm...
68 days. That’s how long attackers are hiding in Australian networks before anyone notices.
Your device management tool just became a weapon. This fortnight: Iran-linked hackers wipe 200,000 devices using Microsoft's own admin tools, an Australian healthcare software vendor hit by ransomware this week,...
Thoughts and articles by Cyooda
All
- All
- Cybersecurity
- Detection Engineering
- How To Guides
- Ransomware Insights
- Security Insights
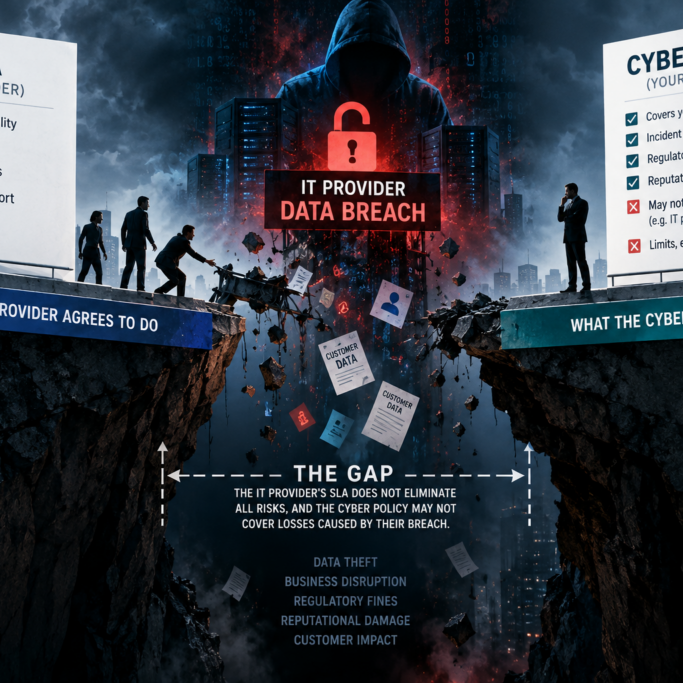
When Your IT Provider Is Part of the Incident
If your firm had a serious cyber incident tomorrow, who would investigate it, who would pay for that, and who would they report to? In most mid-sized firms the honest...
The Invoice Was Real. The Bank Details Were Not
The invoice was genuine. The matter was genuine. The email came from the right firm, in the right thread, with the right signature block. Only the account number had changed....
How Far Back Can Your Firm Actually See?
There is one question I ask in a first meeting that changes the temperature of the room. If someone had been reading your partners' email since March, how far back...

Your Help Desk Is the Easiest Way Into Your Firm
Your Help Desk Is the Easiest Way Into Your Firm I'll tell you how a recent engagement actually went, because the result deserves to be uncomfortable. We were engaged to...
Cybersecurity news from around the world
Phishers Target Aviation Execs to Scam Customers
KrebsOnSecurity recently heard from a reader whose boss's email account got phished and was used to trick one of the company's customers into sending a large payment to scammers. An...
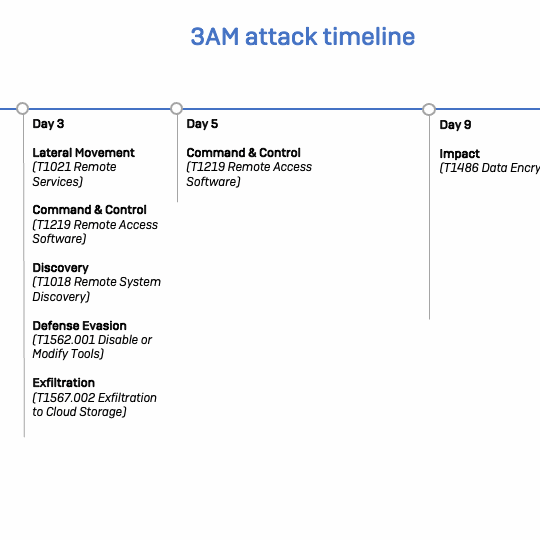
A familiar playbook with a twist: 3AM ransomware actors dropped virtual machine with vishing and Quick Assist
Ransomware is usually a crime of opportunity. Attackers typically strike through an easily discovered vulnerability or security weakness- unpatched Internet-facing software, vulnerable network edge devices, or exposed inbound virtual private...
Android gets patches for Qualcomm flaws exploited in attacks
Google has released security patches for six vulnerabilities in Android's August 2025 security update, including two Qualcomm flaws exploited in targeted attacks. The two security bugs, tracked as CVE-2025-21479 and...
Storm-2603 Exploits SharePoint Flaws to Deploy Warlock Ransomware on Unpatched Systems
Microsoft has revealed that one of the threat actors behind the active exploitation of SharePoint flaws is deploying Warlock ransomware on targeted systems. The tech giant, in an update shared...

Customer Account Takeovers: The Multi-Billion Dollar Problem You Don’t Know About
Everyone has cybersecurity stories involving family members. Here's a relatively common one. The conversation usually goes something like this: "The strangest thing happened to my streaming account. I got locked...
RansomHub Went Dark April 1; Affiliates Fled to Qilin, DragonForce Claimed Control
Cybersecurity researchers have revealed that RansomHub's online infrastructure has "inexplicably" gone offline as of April 1, 2025, prompting concerns among affiliates of the ransomware-as-a-service (RaaS) operation. Singaporean cybersecurity company Group-IB...
What you should be doing when you receive an unsolicited One Time Passcode
If you receive an unsolicited One Time Passcode (OTP) for a service that you use, either as an SMS or Email you should be concerned and act immediately! Why should...
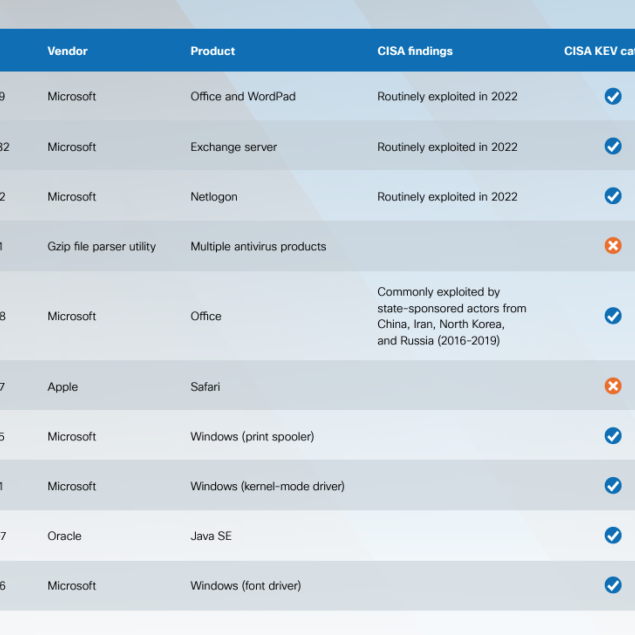
Top targeted vulnerabilities of 2023: STOP this madness
In 2023 the top 10 targeted vulnerabilities used by threat actors to actively exploit victims were more than 10 years old! In order of CVE ranking we have: CVE-2017-0199 -...
Lvl 17, Angel Place,
123 Pitt Street,
Sydney
NSW 2000
(02) 7230 1350
The Legal Cyber Brief — monthly cyber intelligence for law firm leaders.